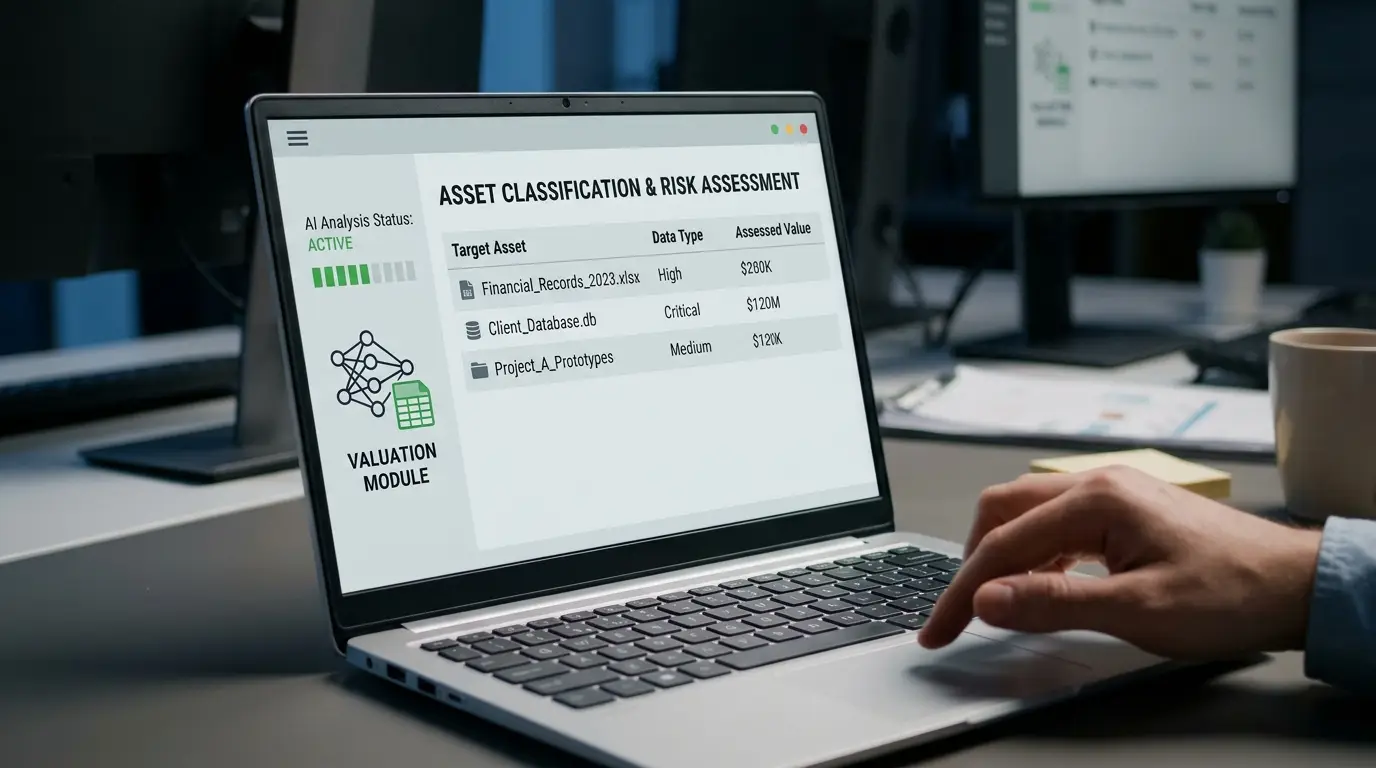
Cybersecurity researchers have uncovered a sophisticated new Windows infostealer that leverages artificial intelligence to prioritize its targets. The malware known as VOLTA or VOLTA AUTODOXER steals credentials and cryptocurrency wallets before sending the harvested data to large language models. This innovative approach allows threat actors to automatically evaluate which victims possess the most valuable assets for monetization.
The Mechanics of AI Driven Theft
The Cisco Talos research team recently published a detailed analysis of this emerging threat. The malware operates by first gathering sensitive information from the infected machine. This includes browser sessions and financial data. Instead of blindly exfiltrating everything the payload constructs a structured dossier and transmits it to an external AI service.
By default the malware utilizes the Claude Opus 4.6 model via the OpenRouter API to analyze the stolen information. The AI generates a custom target assessment that ranks the victim based on potential financial yield. This automated triage allows attackers to focus their extortion or fraud efforts on the most profitable individuals.
| Malware Characteristic | Technical Implementation | Strategic Advantage |
| Primary Payload | Windows credential and session harvester | Comprehensive initial data gathering |
| AI Integration | OpenRouter API connecting to Claude Opus 4.6 | Automated financial valuation of stolen data |
| Fallback Mechanism | Switches to Gemini or Kimi models upon refusal | Ensures continuous operation despite API blocks |
| Evasion Tactic | Complete self deletion after assessment generation | Removes forensic evidence from the host system |
Evasion and Adaptability
The architects of this malware designed it with robust evasion capabilities. Once the AI model returns the victim assessment the payload immediately deletes itself from the host system. This self deleting behavior significantly complicates forensic investigations and endpoint detection efforts.
Furthermore the malware includes built in redundancy. If the primary AI model rejects the malicious prompt due to safety filters the system automatically switches to alternative models like Google Gemini or Kimi. Researchers also noted that the malware can bypass the AI evaluation step entirely if network conditions require a faster exfiltration process.
Implications for Enterprise Security
This development marks a concerning evolution in automated cybercrime. Threat actors are no longer just using AI to write malicious code. They are integrating it directly into the attack chain to optimize their return on investment. Organizations must update their data loss prevention strategies to detect unusual outbound API calls to third party AI services.
Security teams should monitor for unexpected network traffic directed at known AI gateway domains. The Tom's Hardware report emphasizes that traditional signature based detection is insufficient against such adaptive threats. Defending against this new class of malware requires behavioral analysis capable of identifying the unique footprint of AI assisted data exfiltration.
Popular news
Nvidia Faces Severe Supply Constraints on Massive China GPU Orders
AI Engineer Embeds 32-Bit RISC-V CPU Directly Into Qwen Model Weights
AI Chip Smugglers Exploit Trade Control Loophole To Bring Banned HBM Into China
AI Data Center Expansion Halted by Overwhelming Voter Rejection in Midterm Elections
Valve Updates Steam Release Rules Following AI Game Surge