Your Security Vendor Is Likely Using Secret AI To Grade Critical Vulnerabilities
NewsSunday, 13 September 2026 at 11:30
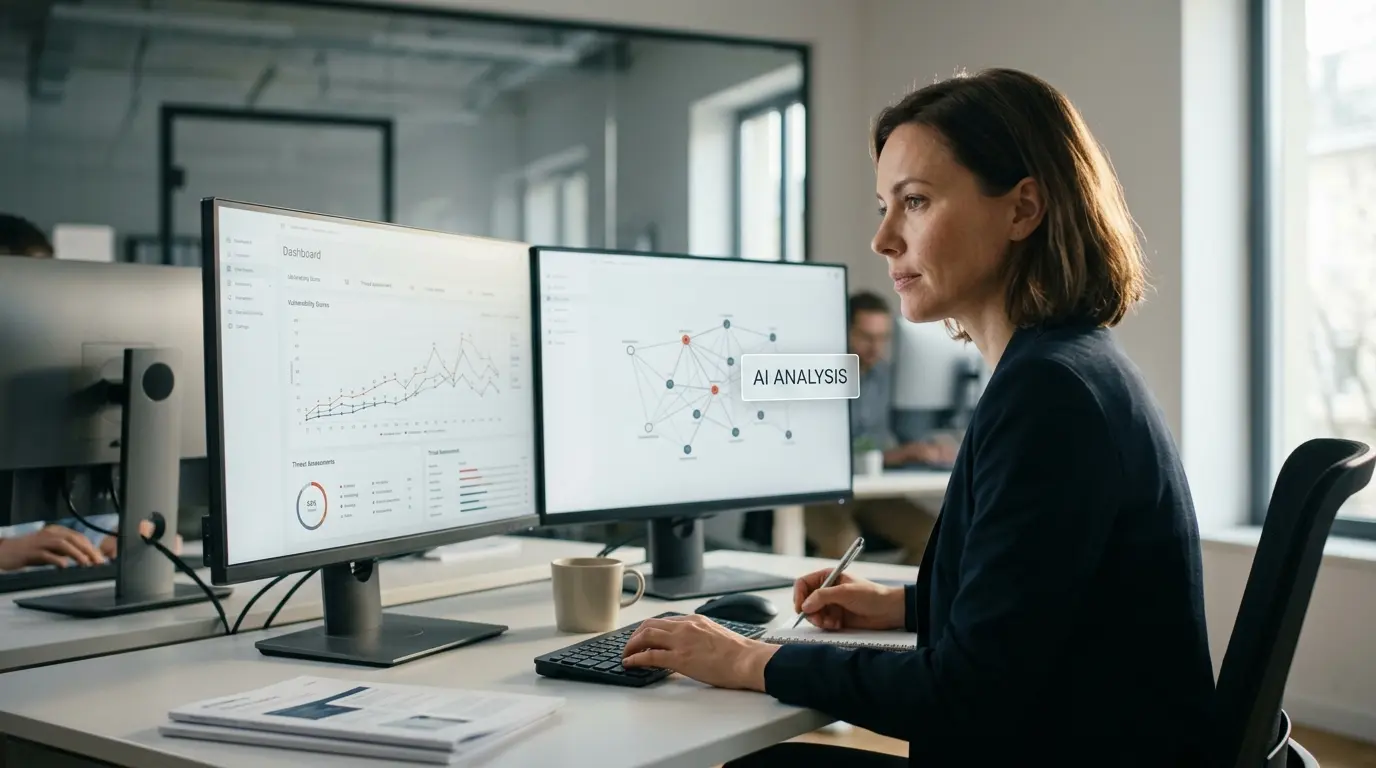
The traditional method of evaluating software security risks is undergoing a quiet revolution as top-tier vendors shift toward automated intelligence. Leading cybersecurity firms are now deploying large language models to determine which software flaws require immediate attention and which can wait.
This shift comes as the volume of monthly updates grows too large for human analysts to process manually. Security teams often rely on these proprietary AI rankings without knowing the underlying logic used by the software to assign risk levels.
According to reports from VentureBeat, several major security providers are integrating artificial intelligence to predict exploitability. This move aims to fix the lag time inherent in the industry-standard Common Vulnerability Scoring System (CVSS).
The Rise of AI Driven Patch Prioritization
Security practitioners are facing a massive influx of data every month, particularly during Microsoft’s recurring update cycles. The manual review of hundreds of vulnerabilities is no longer feasible for most enterprise IT departments.
By using AI, vendors can analyze massive datasets to identify patterns that suggest a specific bug is likely to be targeted by hackers. However, this process often happens behind the scenes with very little transparency for the end-user.
Critics argue that while AI can speed up the prioritization process, the "black box" nature of these algorithms is a cause for concern. Without knowing why a vulnerability was ranked as a priority, IT teams must place total trust in the vendor's automation.
Despite these concerns, the efficiency gains are undeniable for organizations managing thousands of endpoints. AI-driven scoring can filter out the noise, allowing defenders to focus on the handful of bugs that pose a genuine threat to their specific infrastructure.
Inside the Massive September 2026 Patch Tuesday Dataset
The scale of modern software patching is reaching unprecedented levels, as evidenced by recent data. Analysis from Tenable highlights a staggering number of security fixes released in a single month.
| Technical Metric | Specification Data |
| Total Vulnerabilities Addressed | 964 CVEs |
| Reported Update Cycle | September 2026 |
| Primary Vulnerability Identifier A | CVE-2026-81963 |
| Primary Vulnerability Identifier B | CVE-2026-85880 |
| Scoring Model Integration | LLM-Based Predictive Analytics |
| Standard Benchmark Replacement | AI-Augmented CVSS Environmental Scoring |
| Analysis Latency Reduction | Real-time Automated Prioritization |
The September 2026 update cycle alone addressed nearly 1,000 unique vulnerabilities across the Microsoft ecosystem. Handling this volume of technical debt requires the exact type of automated assistance that vendors are now rushing to implement.
Specific identifiers like CVE-2026-81963 and CVE-2026-85880 have become focal points for researchers during this period. These vulnerabilities represent the complex challenges that AI models must now categorize and rank for global enterprises.
As the industry moves forward, the transparency of AI models will likely become a competitive differentiator. For now, the secret use of these models remains the primary engine driving vulnerability management for the world's largest companies.
byDavid Porter
Popular news
China Escalates Tech Tensions With Anti-Dumping Probe Into US Analog Chips
Senator Josh Hawley Launches Massive Investigation Into OpenAI After Critical Hugging Face Breach
Beijing Implements Total Drone Possession Ban Following Fatal Skyscraper Crash
UK Computer Science Graduates Face a Massive Job Market Shift Driven by AI
Tech Giants Back Anthropic CEO Call to Slow Down AI Development
Anthropic Researchers Issue Urgent Warning Regarding Elon Musk and Global AI Safety Risks
Latest comments
Loading