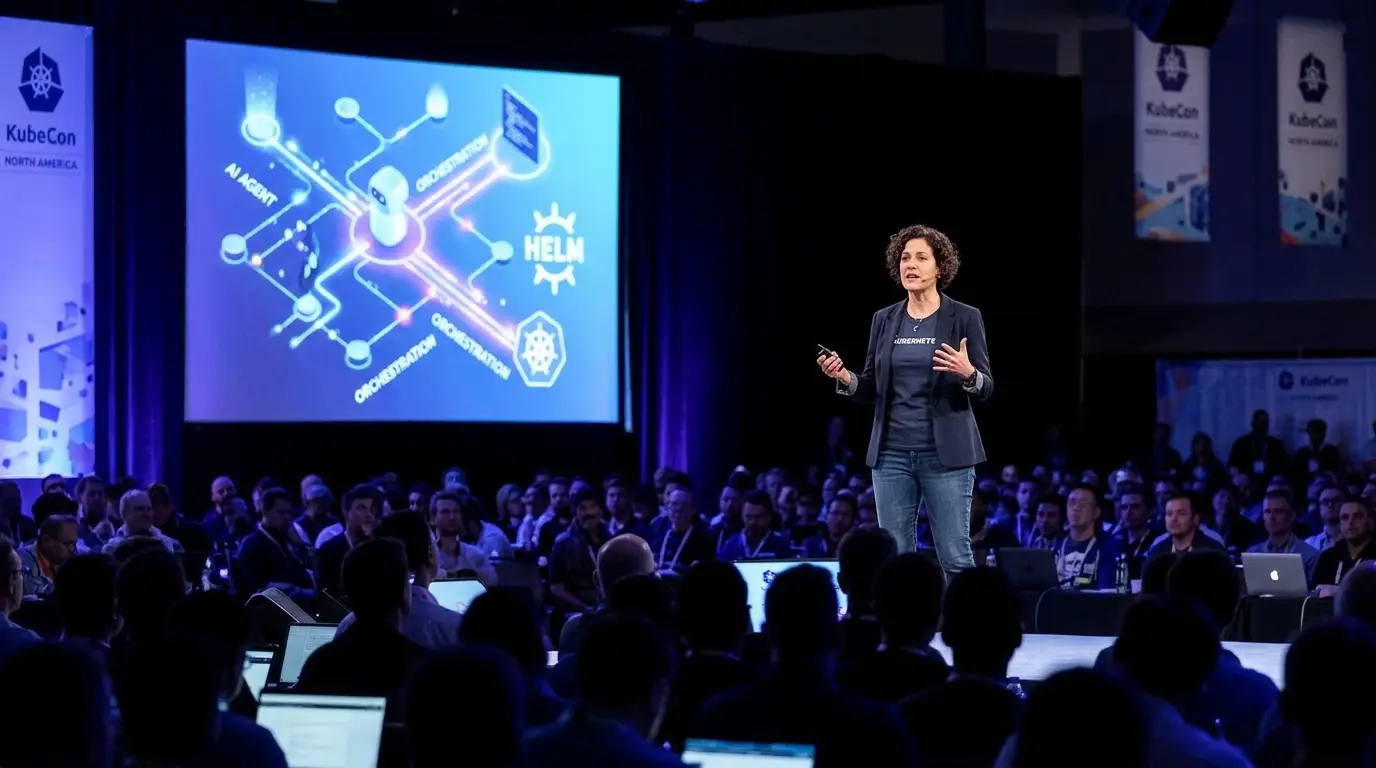
Kubernetes has firmly established itself as the default container orchestration standard across enterprise environments. The cloud native community is now gathering at KubeCon and CloudNativeCon North America in Salt Lake City to address the next major infrastructure challenge. Autonomous AI agents are transitioning from simple query responses to executing complex business systems. This evolution demands strict control over what these agents are permitted to access and modify. Industry leaders recognize that relying solely on language model guardrails is insufficient for secure production environments.
Introducing OpenShell for Agent Safety
To solve this critical security gap, Red Hat and Nvidia are jointly developing OpenShell. This open source secure agent runtime is designed specifically for Kubernetes environments. The project establishes hard boundaries around agent execution, ensuring that autonomous systems operate within predefined sandboxed environments. According to official Red Hat documentation, OpenShell provides a safe and private runtime for fleets of autonomous AI agents by delegating pod creation and management to isolated workload systems. This approach prevents unauthorized file access or package installations while maintaining the flexibility agents need to perform useful tasks. TheCUBE research team highlighted this development as a central theme for the next chapter of cloud native computing as detailed in recent industry coverage.
| Technology Component | Primary Function in AI Orchestration |
| Kubernetes Scheduler | Allocates compute resources for distributed AI training and inference |
| OpenShell Runtime | Enforces strict sandboxing and access controls for autonomous agents |
| CNCF AI Conformance | Validates interoperability and security standards for AI platforms |
| GPU Orchestration Tools | Manages hardware acceleration and resource sharing across containers |
| Multicloud Portability | Ensures consistent agent deployment across hybrid infrastructure |
Industry Collaboration and Standardization
The push for secure AI orchestration extends beyond individual vendors. The Cloud Native Computing Foundation recently introduced initiatives to standardize AI and machine learning workload deployment across Kubernetes clusters to ensure interoperability. This ensures consistent security postures for enterprises running distributed AI infrastructure. During the event, theCUBE livestreaming studio will host exclusive interviews with executives from Red Hat and Nvidia to explore these innovations in GPU orchestration and platform engineering. Companies are actively building Kubernetes native tools to support workload portability across diverse multicloud environments.
Preparing for Production Scale
Enterprises must balance agent autonomy with rigorous operational control. The integration of secure runtimes like OpenShell into broader AI platforms represents a significant step toward trustworthy automation. Organizations can now deploy autonomous agents with confidence, knowing that underlying infrastructure enforces strict compliance rules. As KubeCon attendees explore these advancements, the focus remains on building resilient systems that scale securely. The future of cloud native computing depends on this precise balance between innovation and governance.
Popular news
PSI Says AI System Solved an 18-Year-Old Quantum Computing Conjecture
Claude’s 'Dreaming' Explained: How AI Memory Works
Airbnb Challenges Traditional Chatbots With AI Travel Agent Planned for 2027
AWS Launches Agentic AI Kiro Bots With Memory And Recurring Job Support
Democratic Lawmakers Push for Artificial Superintelligence Ban After Midterm Wins