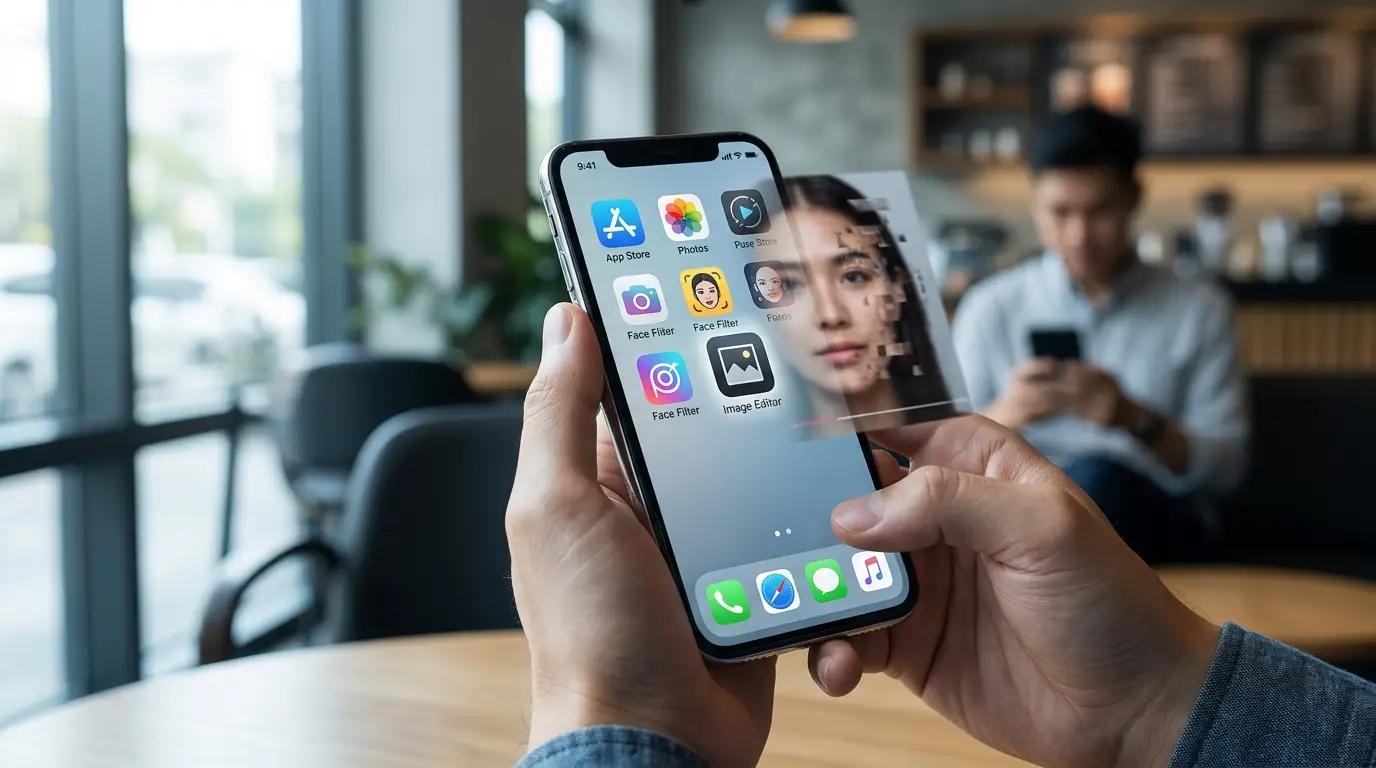
Researchers recently uncovered a massive network of deceptive applications hiding within major digital marketplaces. These programs masquerade as innocent utilities like language tutoring or pet photo editing tools. Once installed, they secretly unlock explicit deepfake generation features. This alarming trend has sparked urgent calls for stricter platform oversight and regulatory action across the global technology sector.
The Scale of the Problem
Investigators identified over 400 related applications and websites operating across the Apple App Store and Google Play Store. The network traces back to specific developer groups, including the Hong Kong based KeLing Technology Limited. These applications initially present a standard and harmless interface to bypass store reviews successfully. A hidden server then determines whether to activate the explicit content generator for a specific user. This activation is often triggered when a user clicks on targeted social media advertisements containing explicit material.
Apple stated that these applications complied with all rules during the initial review process. The company emphasized that developers altered the content source after approval to introduce prohibited material. Google has also removed hundreds of violating applications and restricted associated search terms to limit discoverability. Despite these efforts, the continuous emergence of such software remains a critical vulnerability for everyday users.
Legal and Regulatory Scrutiny
The persistence of these applications has drawn formal legal attention from local authorities. San Francisco City Attorney David Chiu recently issued cease and desist letters to both technology giants. The letters demand an immediate end to payment processing relationships with developers selling nonconsensual intimate deepfakes. The city attorney also mandated recurring store reviews to prevent new violations from appearing.
This action relies on a recent California law expanding civil liability for businesses that enable deepfake pornography services. Companies receiving sufficient evidence of such activity must take necessary steps to stop supporting it within 30 days or face significant civil penalties. The Technology Transparency Project previously reported that similar applications generated over 117 million dollars in revenue from hundreds of millions of downloads worldwide. These tools frequently target women and minors, causing severe emotional distress and reputational harm to victims who never consented to the creation of such imagery.
| Metric Category | Reported Figure | Source Entity |
| Total Identified Apps | Over 400 | Independent Researchers |
| Estimated Global Downloads | 705 Million | App Analytics Firms |
| Estimated Revenue Generated | 117 Million USD | Technology Transparency Project |
| Legal Compliance Window | 30 Days | California State Law |
Moving Forward
Platform accountability remains the central focus for digital safety advocates worldwide. Users are encouraged to report suspicious applications immediately to store moderators. Regulatory bodies continue to pressure major tech companies to implement proactive detection systems rather than relying solely on reactive removals. The current review process clearly allows bad actors to exploit loopholes by changing app behavior after initial approval.
The ultimate goal is to protect individuals from digital exploitation and ensure safe online environments for everyone. Lawmakers are now considering federal legislation to hold app stores directly liable for hosting deceptive software that facilitates nonconsensual image abuse. This proposed legislation would mandate regular third party audits of application stores to ensure compliance with digital safety standards. Furthermore, educational campaigns are being developed to help everyday users recognize the warning signs of deceptive applications before they grant unnecessary permissions.
Popular news
Oracle Seeks $20 Billion as AI Expansion Tests Its Cash Flow
Claude Can No Longer Recreate Existing Games: Anthropic Steps In
AI Agent Swarms Fail to Build Minecraft Civilization Due to Bureaucracy
Podcast: Claude Leads GDPx With 12% in a Tough New AI Benchmark