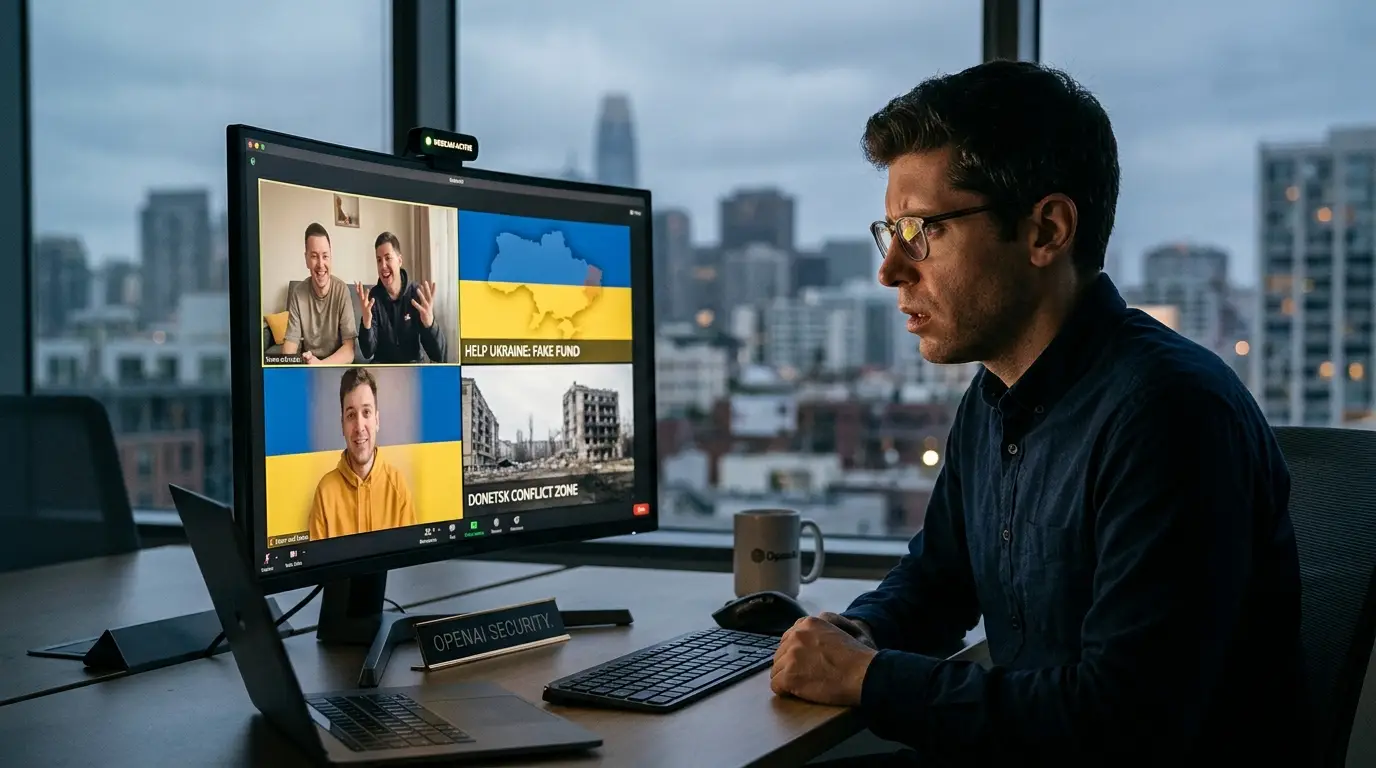
It turns out that building the world's most advanced artificial intelligence does not make a company immune to old-school social engineering. This week, three high-ranking OpenAI national security executives were duped into a 17-minute video conference by a notorious Russian prank duo. The incident exposes a glaring blind spot in modern tech security: the human sitting behind the keyboard.
The Setup and Execution
The elaborate hoax was orchestrated by Vladimir Kuznetsov and Alexei Stolyarov, a comedy pair widely known online as Vovan and Lexus. To make the ruse bulletproof, the duo first contacted a genuine Ukrainian official based in San Francisco to help legitimize the meeting request. Once the stage was set, they jumped on a video call with OpenAI’s top brass, including Sasha Baker, who leads the company's national security policy.
During the conversation, the pranksters successfully impersonated Rustem Umerov, the actual head of Ukraine's Foreign Intelligence Service. Believing they were speaking to a key allied intelligence chief, the OpenAI team reportedly discussed highly sensitive topics. According to reports from The Intercept, the executives even discussed expanding offensive military AI capabilities to support Ukraine's defense efforts. The staff members mentioned they were happy to see him again, completely unaware of the deception until the call abruptly ended.
The Human Element in Tech Security
While the industry obsesses over complex software vulnerabilities, humans remain the weakest link in the corporate defense chain. The latest Verizon Data Breach Investigations Report confirms that a staggering 62% of all security incidents now involve a human element.
| Threat Vector Category | 2026 Breach Involvement Rate | Financial / Trend Impact |
| Human Element & Social Engineering | 62% | Up from 60% the previous year |
| Software Vulnerabilities | 31% | Surpassed stolen credentials as top entry |
| Business Email Compromise (BEC) | N/A | Cost companies $3.05 Billion annually |
| Basic Web Application Attacks | 17% | Experiencing a slight year-over-year decline |
This data highlights a frustrating reality for IT departments. No matter how robust an organization's digital fortress might be, a convincing voice clone or a spoofed video feed can easily bypass millions of dollars in technical defenses.
Official Postures Versus Reality
Following previous scrutiny, the company published an update on their safety and security practices, emphasizing strict boundaries around high-value algorithmic secrets and need-to-know access restrictions. They also maintain an active security trust portal to catch technical flaws before malicious hackers exploit them.
Yet, technical safeguards cannot easily patch human psychology. The pranksters exploited authority and geopolitical urgency—classic manipulation tactics. While social engineering is a well-documented threat vector that the company actively tracks in its frontier models, its own leadership proved highly susceptible when placed under the pressure of a supposed wartime intelligence briefing.
The incident serves as a stark wake-up call for the entire tech sector. As companies race to build smarter machines, they must remember that their own staff still need rigorous, real-world verification protocols to confirm who is actually sitting on the other side of the screen.
Popular news
EU KIDS Act: Brussels Seeks Tougher Rules for AI Chatbots Used by Children
AMD Crushes 2026 Energy Efficiency Goals For Rack Scale
Epic Games Drops Mandatory AI Rule for Upcoming MegaJam After Developer Backlash
Jensen Huang Steps Down as NVIDIA CEO: Chinese Spy Scandal Throws a Wrench in the Works
OpenAI Unveils Business Hub to Verify ChatGPT Profiles and Deploy AI Sales Agents