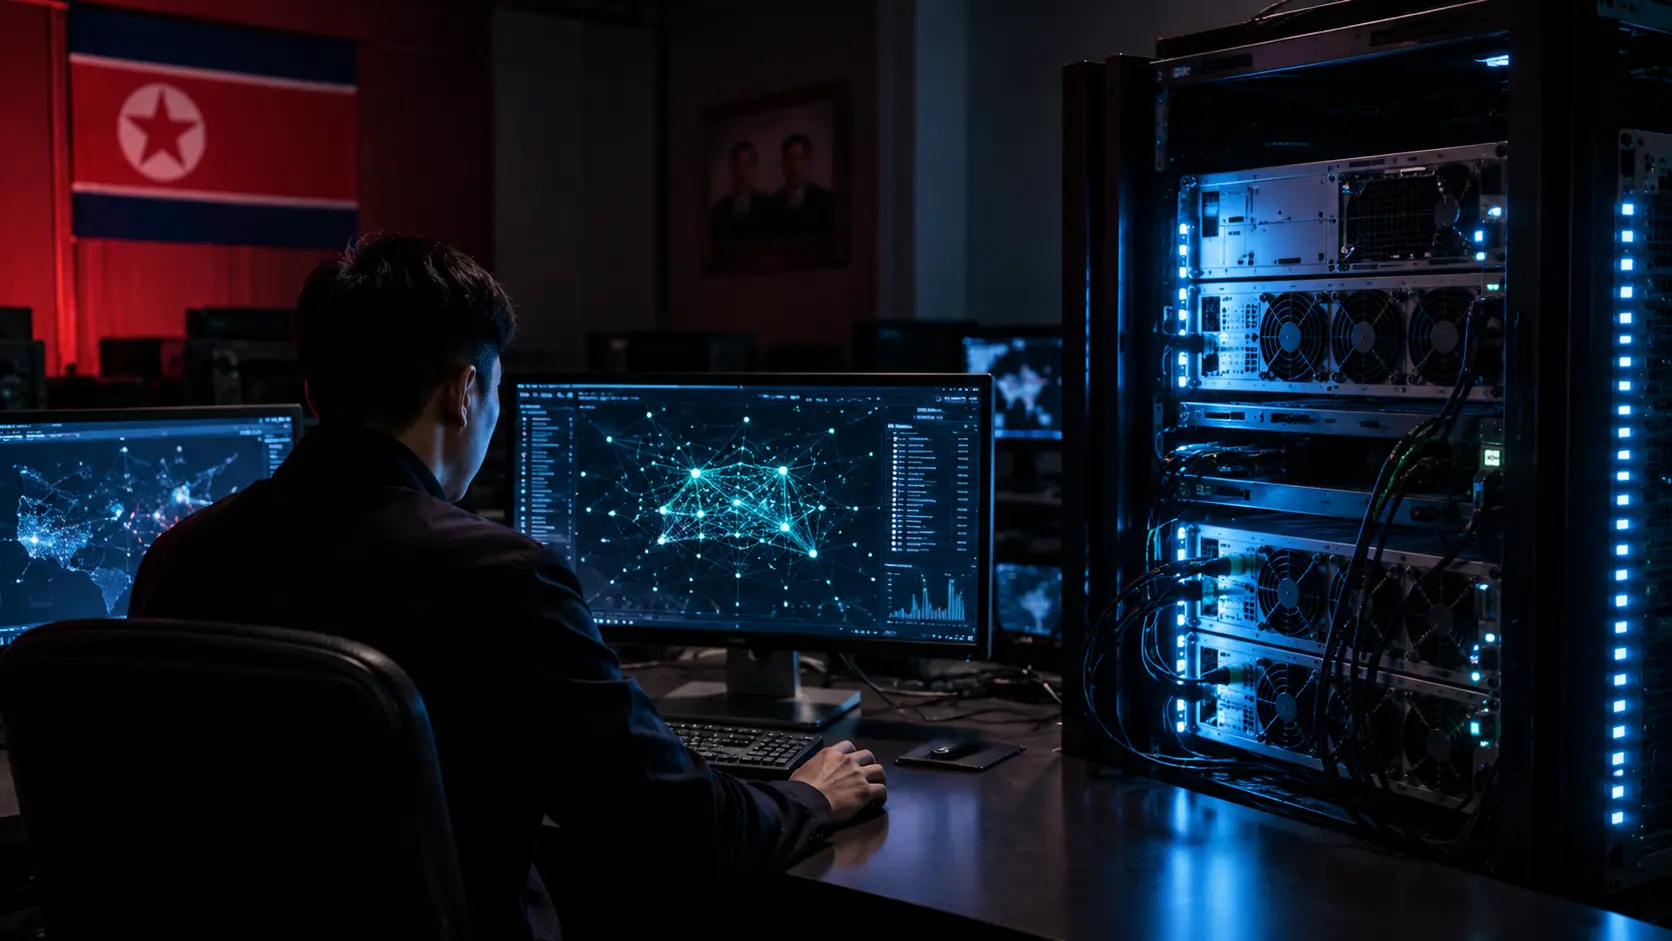
The North Korea–linked hacking group Kimsuky has built a local AI setup designed to aid phishing, analyze stolen data, and automate parts of cyberattacks.
That’s according to South Korean cybersecurity firm Genians, which told Reuters it traced the infrastructure to the group. Researchers found tools including Ollama, GPT4All, Msty, the AI coding app Cursor, and technology for retrieval augmented generation, commonly known as RAG.
The findings have not been independently verified. They also don’t prove Kimsuky is already running fully autonomous AI-driven attacks. But the research shows state-backed hackers can combine off-the-shelf AI software into a private workspace with little oversight from foreign AI providers.
Why is Kimsuky using local models?
Services like ChatGPT, Gemini, and Claude mostly run on the provider’s servers. Prompts and any uploaded data are sent to an external platform.
That’s risky for a hacking group. Providers can flag suspicious prompts, block accounts, and retain information that could surface in an investigation.
Local AI models run on machines or servers controlled by the user. Sensitive or stolen data therefore doesn’t need to be sent to OpenAI, Google, Anthropic, or any other outside party.
Ollama and GPT4All make it relatively easy to run available models locally. Msty provides an interface to manage multiple local and online models from a single environment.
A group doesn’t need to train a language model from scratch. Existing models can be downloaded and tailored to specific tasks with additional software.
That sharply lowers both cost and technical barriers.
RAG can turn stolen files into a searchable trove
Genians also found technology for retrieval augmented generation. With RAG, a language model is paired with a separate corpus of documents.
When a user asks a question, the system first retrieves relevant passages from those documents. The model then uses that information to craft a response.
Companies use RAG to let employees query internal manuals, contracts, or customer records. A hacking group can apply the same method to stolen data.
After a successful breach, an organization can lose thousands of files. Manually reading and sorting them is time-consuming. With RAG, attackers can ask which documents contain passwords, which employees have access to sensitive systems, or which files include valuable technical details.
The AI model doesn’t need to have seen the documents during its original training. The information is retrieved at query time and added to the context.
That makes RAG particularly useful for espionage and digital theft.
From basic phishing to a full AI toolkit
Criminals have long used generative AI to write phishing messages. A model can fix typos, translate text, or tailor a message to a target’s role and background.
Genians says Kimsuky is moving beyond that. The discovered software stack points to a broader infrastructure supporting multiple phases of a cyber operation.
The systems could potentially be used for:
- Summarizing and classifying stolen documents
- Writing convincing phishing emails
- Creating fake financial and business documents
- Analyzing large volumes of exfiltrated data
- Generating or modifying code
- Transcribing recorded conversations
- Automating discrete attack steps
Genians also found documents about investments, finance, and cryptocurrencies that may have been produced with AI. Such files can be sent as lures.
A victim might think they’re receiving an investment report or business proposal. The file or a linked website then tries to steal login credentials or install malware.
Who is Kimsuky?
Kimsuky is a hacking group that U.S. and South Korean authorities link to the North Korean government.
The group focuses primarily on digital espionage. Targets include governments, think tanks, defense organizations, journalists, and experts working on North Korea.
The U.S. Treasury sanctioned Kimsuky in 2023, saying the group gathers intelligence that supports the North Korean regime’s strategic objectives.
Other North Korean groups have also been linked to financial theft and attacks on crypto firms. Proceeds from cybercrime are believed to help fund the North Korean state.
North Korea routinely denies allegations of involvement in international cyberattacks.
Local AI is hard to police centrally
Major AI providers can curb abuse on their own platforms. They can scan prompts, block dangerous outputs, and shut down accounts showing suspicious behavior.
Many of those safeguards don’t exist for locally run models. The original developer typically has no direct visibility into how a downloaded model is used.
That doesn’t make local AI inherently dangerous. Companies use local models precisely to keep trade secrets, personal data, and other sensitive information inside their own infrastructure.
But the same privacy features appeal to attackers. A model that doesn’t send data to external servers leaves fewer traces with any provider that could detect misuse.
This is the core tension with open, downloadable AI. The tech gives businesses and developers more control, while limiting the ability to stop abuse from a central point.
No evidence yet of fully autonomous attacks
The discovered software doesn’t prove that Kimsuky deploys an AI agent to independently hack entire organizations.
Successful attacks still require infrastructure, access tools, technical expertise, and operational decisions. AI-generated code can also contain errors and even expose an attack.
But the tools don’t need to be fully autonomous to have impact. If AI helps researchers analyze documents faster, craft better phishing messages, and adapt malware, the same group can hit more targets at once.
The immediate risk is scale. Tasks that once took hours of manual work can be done faster and cheaper.
For organizations, that means traditional warning signs are less reliable. A phishing email with clean language and convincing personal details is no longer a sure marker of a meticulous human operator.
Staff should look beyond typos to unexpected requests, suspicious links, odd domain names, and attempts to extract login credentials or payments.
The Kimsuky case ultimately shows that local AI isn’t just for privacy-minded businesses and hobbyists. Professional hackers are now building their own AI stacks—well outside the reach of big commercial platforms.
Popular news

Anthropic Researchers Warn Advanced AI Models Could Trigger Human Extinction

Andy Burnham Faces Urgent Demands to Block Artificial Superintelligence in Manchester

Anthropic Researchers Issue Urgent Warning Regarding Elon Musk and Global AI Safety Risks

OpenAI Board Member Paul Christiano Warns AI Control Could Be Lost Forever

Senator Josh Hawley Launches Massive Investigation Into OpenAI After Critical Hugging Face Breach

UK Computer Science Graduates Face a Massive Job Market Shift Driven by AI
Latest comments
Loading