EU AI Act Compliance Checklist: Fines and Enforcement
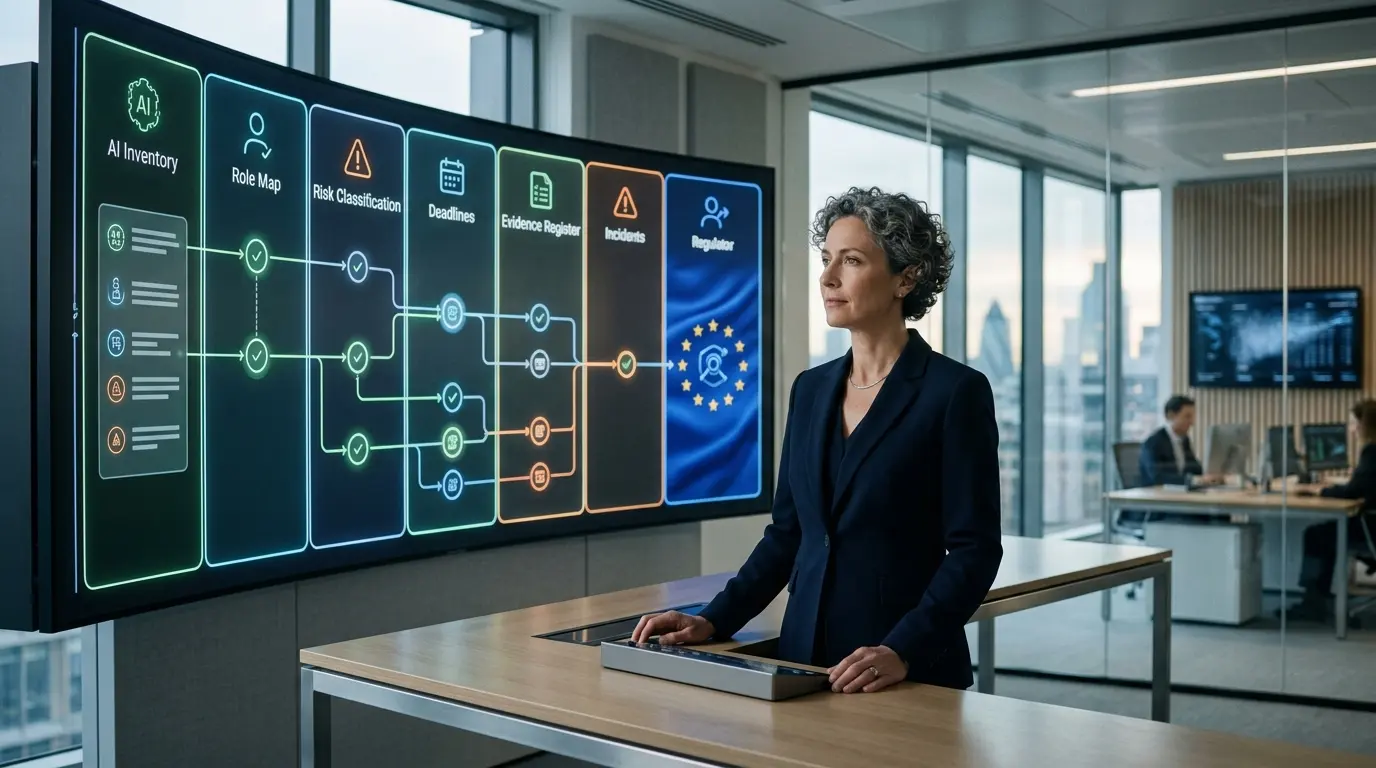
EU AI Act compliance is not one policy, one course or one risk label. It is a portfolio-management process connecting every relevant AI system and model to its legal role, intended purpose, risk category, applicable date, technical controls, operational owner and evidence.
As of August 2026, several obligations are already enforceable: the original prohibited practices, Article 4 AI literacy, GPAI model rules and Article 50 transparency. The new sexual-content prohibitions apply in December 2026. The principal high-risk system requirements arrive in December 2027 and August 2028.
A good program therefore does two things at once:
- meets obligations already in force; and
- builds the longer technical and conformity work before future deadlines.
For the law’s structure, read our complete EU AI Act guide. For the exact sequence, use the EU AI Act timeline.
Compliance checklist at a glance
| Workstream | Minimum output | Status question |
| Governance | Named accountable owner and decision forum | Who can approve, restrict or stop AI? |
| Inventory | Complete system/model register | Do we know where AI is used, including shadow AI? |
| Scope and roles | Documented Article 2 and role analysis | Are we provider, deployer, importer, distributor, manufacturer or GPAI provider? |
| Prohibited practices | Article 5 screening | Is any current or foreseeable practice forbidden? |
| Risk classification | Annex I, Annex III, Article 6(3), Article 50 and GPAI analysis | Which legal layers apply? |
| AI literacy | Role-based Article 4 measures and records | Do relevant people understand the systems and risks? |
| Transparency | Notices, technical marks and disclosure controls | Are interaction and synthetic content disclosed correctly? |
| GPAI | Article 53/55 evidence and AI Office route | Are we a model provider or downstream integrator? |
| High-risk readiness | Requirements, conformity and deployer plan | Can we meet 2027 or 2028 obligations? |
| Vendor management | Evidence and change rights | Can suppliers support our statutory duties? |
| Monitoring and incidents | Logs, complaints, reporting and corrective action | Will we detect and respond to failure? |
| Enforcement readiness | Organized evidence and authority contacts | Can we explain the program quickly and accurately? |
1. Establish accountability
Name an executive sponsor and operational owner. Then define who has authority to:
- approve a new AI use;
- classify a system or model;
- accept residual risk;
- block an unsafe deployment;
- require vendor evidence;
- report a serious incident;
- respond to authorities;
- and retire a system.
The AI Act does not require one universal “AI officer,” but fragmented responsibility is still a governance failure. A practical structure can include legal/compliance, product, IT, security, privacy, procurement, HR, risk and relevant business owners.
Record decisions and disagreements. A committee without decision rights is not accountability.
2. Build a complete AI inventory
Inventory is the foundation of every other step. Include more than large language models and visible chatbots.
Look for:
- embedded AI in SaaS products;
- automated scoring or ranking;
- biometric and emotion features;
- recommendation and personalization;
- fraud and anomaly detection;
- image, audio and video generation;
- call automation and voice cloning;
- computer vision;
- internally developed models;
- vendor APIs;
- open-source models;
- agentic workflows;
- and AI used by contractors.
For each item, record:
- unique ID and owner;
- vendor and legal entity;
- system, model and version;
- intended purpose and actual use;
- users and affected persons;
- countries and business entities;
- data categories;
- decisions influenced;
- autonomy and human oversight;
- market or deployment date;
- upstream models and downstream integrations;
- and current status.
Create a route for employees to declare unapproved tools without punishment being the only outcome. Otherwise shadow AI stays hidden.
3. Determine whether the object is in scope
Document whether the artifact is:
- an AI system;
- a general-purpose AI model;
- a component of another system;
- ordinary deterministic software;
- or a regulated product containing AI.
Then test Article 2 scope, including:
- EU establishment or deployment;
- placement on the EU market;
- output used in the EU;
- personal non-professional use;
- research and pre-market development;
- national security, military and defense exclusions;
- and relevant open-source treatment.
Do not force every software tool into the Act. Equally, do not exclude a system because the vendor avoids the word “AI.” Preserve the technical and legal reasoning.
4. Assign operator roles
For each object, identify every relevant actor:
- AI system provider;
- deployer;
- importer;
- distributor;
- product manufacturer;
- authorized representative;
- GPAI model provider;
- and affected persons.
One organization can have several roles. Reassess after:
- rebranding;
- significant model modification;
- substantial system modification;
- changed intended purpose;
- acquisition or legal-entity changes;
- and new EU market placement.
Use our providers and deployers guide to map the value chain and contract handoffs.
5. Screen prohibited practices
Complete an Article 5 assessment before other risk classification.
Test for:
- harmful manipulation or deception;
- exploitation of age, disability or social/economic vulnerability;
- prohibited social scoring;
- criminal-risk prediction based solely on profiling or personality;
- untargeted facial-image scraping;
- workplace or education emotion recognition;
- sensitive biometric categorization;
- most real-time law-enforcement biometric identification in public spaces;
- non-consensual intimate synthetic material;
- and child sexual abuse material.
Where a condition may apply:
- pause deployment;
- map each legal element;
- verify any exception narrowly;
- evaluate foreseeable misuse and guardrail circumvention;
- redesign or stop the use;
- document approval and review triggers.
Read the prohibited-practices guide for the detailed conditions and December 2026 additions.
6. Classify the remaining systems and models
For each permitted system, complete separate tests.
High-risk route
- Is it a safety component of, or itself, an Annex I regulated product requiring third-party conformity assessment?
- Is its intended purpose listed in Annex III?
- Can Article 6(3) apply?
- Does it perform profiling, which prevents reliance on that exclusion?
- Has the provider documented and registered any non-high-risk conclusion?
Transparency route
- Does it interact directly with people?
- Does it generate or manipulate synthetic content?
- Is emotion recognition or biometric categorization deployed?
- Is a deepfake published?
- Is AI text published to inform the public on a matter of public interest?
GPAI route
- Is a GPAI model placed on the EU market?
- Who is its provider?
- Is an open-source exemption relevant?
- Has the model been significantly modified?
- Does systemic risk apply?
The risk-categories guide provides one decision tree across these layers.
7. Implement Article 4 AI literacy
Providers and deployers must take measures supporting AI literacy among relevant staff and other people operating or using systems on their behalf.
Your evidence should show:
- target groups identified from the inventory;
- existing knowledge and experience considered;
- system and context risks considered;
- baseline guidance delivered;
- role-specific learning for higher-impact uses;
- contractors covered where relevant;
- human-oversight staff trained;
- and refresh triggers defined.
No universal course, certificate or AI officer is mandated. The measures must nevertheless be real and proportionate.
Use the Article 4 AI literacy guide to build the role matrix and evidence file.
8. Implement Article 50 transparency
For every relevant workflow, assign both provider and deployer controls.
Provider controls
- direct-interaction notice designed into the system;
- obviousness assessment where relying on the exception;
- machine-readable marking for generated or manipulated content;
- robustness and interoperability tests;
- technical documentation;
- and support for downstream preservation.
Deployer controls
- notices for emotion recognition and biometric categorization;
- visible deepfake disclosure;
- public-interest text disclosure or documented human-review exception;
- accessible and timely presentation;
- preservation of provenance;
- and publication approval.
The limited December 2, 2026 transition applies only to Article 50(2) marking for generative systems already on the market before August 2, 2026.
Use our Article 50 transparency guide for examples and the voluntary Code.
9. Meet GPAI model obligations
Where your organization is a GPAI model provider, complete Article 53 work:
- technical documentation;
- downstream-provider information;
- EU copyright-compliance policy;
- public summary of training content;
- authorized representative where required;
- and AI Office submission process.
For models with systemic risk, add:
- state-of-the-art evaluations;
- adversarial testing;
- systemic-risk assessment and mitigation;
- serious-incident reporting;
- and adequate cybersecurity for the model and infrastructure.
Decide whether to sign the voluntary GPAI Code of Practice or demonstrate compliance through alternative adequate means.
If you are a downstream provider, request the evidence needed for your own system. The GPAI guide explains the model-versus-system distinction.
10. Prepare high-risk systems before the deadline
For each current or planned high-risk system, create a delivery plan covering Articles 8–15:
- lifecycle risk management;
- training, validation and testing data governance;
- technical documentation;
- automatic logging and traceability;
- transparency and instructions for deployers;
- human oversight;
- accuracy targets;
- robustness;
- and cybersecurity.
Provider program:
- quality-management system;
- conformity route;
- standards mapping;
- EU declaration and CE marking where required;
- registration;
- post-market monitoring;
- incident reporting;
- corrective action;
- and document retention.
Deployer program:
- instructions and allowed-use controls;
- input-data quality;
- trained oversight;
- local monitoring and logs;
- worker and affected-person notices;
- fundamental-rights impact assessment where required;
- and suspension and escalation procedures.
The main Annex III date is December 2, 2027; the Annex I product date is August 2, 2028. Use our high-risk AI systems guide to avoid treating those dates as the start of work.
11. Integrate GDPR, security and sectoral law
The AI Act does not replace other obligations. Build one control map covering, where relevant:
- GDPR lawful basis, transparency, minimization, rights and DPIAs;
- employment and worker consultation;
- anti-discrimination law;
- consumer protection;
- product safety and medical-device rules;
- cybersecurity and the Cyber Resilience Act;
- NIS2;
- copyright and trade secrets;
- the Digital Services Act;
- accessibility;
- and sector-specific financial, health, transport or public-sector requirements.
Cross-reference shared evidence instead of creating inconsistent copies. A fundamental-rights impact assessment can incorporate relevant DPIA material, but the two assessments are not identical.
12. Strengthen vendor and value-chain contracts
Procurement should require more than a generic promise of “AI Act compliance.”
Include clauses for:
- legal roles and intended purpose;
- prohibited and unsupported uses;
- model and system versions;
- technical documentation and instructions;
- evaluation and performance evidence;
- high-risk support;
- Article 50 marking and disclosure features;
- log access and retention;
- security controls;
- incidents and regulatory reporting;
- change, fine-tuning and deprecation notices;
- audit and authority cooperation;
- subcontractors and upstream models;
- corrective action, recall and termination;
- and intellectual-property and trade-secret safeguards.
Create minimum evidence gates by risk. A low-impact drafting tool and a high-risk recruitment system should not pass the same procurement checklist.
13. Build change management
AI systems change through model updates, prompt changes, retrieval sources, fine-tuning, new tools and vendor configuration. Require reassessment when:
- intended purpose changes;
- a new affected group appears;
- a human-review step is removed;
- the model or major version changes;
- autonomy expands;
- new data is used;
- the system moves into another country or legal entity;
- branding changes;
- performance degrades;
- or an incident reveals a different risk.
The change record should test whether:
- classification changes;
- the organization becomes a provider;
- conformity assessment must be repeated;
- Article 50 notices change;
- or new training is needed.
14. Monitor performance, incidents and complaints
Create one operational process connecting:
- system monitoring;
- security alerts;
- bias and error metrics;
- user and affected-person complaints;
- vendor notifications;
- serious-incident assessment;
- regulatory reporting;
- corrective action;
- and lessons for AI literacy.
Define severity and escalation criteria before an incident. Teams should know:
- who can suspend the system;
- who preserves logs and evidence;
- who contacts the provider;
- who assesses GDPR and sector reporting;
- who decides whether the AI Office or national authority must be notified;
- and who communicates with affected people.
Test the process through tabletop exercises.
15. Maintain an audit-ready evidence register
A regulator should be able to follow the logic from inventory to control.
For each system or model, retain:
- identity and version;
- scope assessment;
- operator-role map;
- intended purpose;
- Article 5 screen;
- risk classification;
- applicable dates;
- vendor documents;
- policies and approvals;
- AI literacy measures;
- Article 50 implementation;
- high-risk or GPAI documentation;
- tests and evaluations;
- logs and monitoring;
- incidents, complaints and corrective action;
- changes and reviews;
- and accountable owners.
Use consistent versioning. Do not overwrite the evidence supporting an earlier release.
16. Know who enforces the Act
Enforcement is shared.
National competent authorities
Member State authorities enforce the rules for most AI systems. National structures can include market-surveillance and notifying authorities and may interact with data-protection, consumer, labor or sector regulators.
European Commission and AI Office
The AI Office enforces rules for GPAI model providers. Following the 2026 Omnibus, it also has competence for specified AI systems, including systems developed by the provider—or a provider in the same business group—of the underlying GPAI model and systems integrated into very large online platforms or search engines under the Digital Services Act.
The AI Office can request information, obtain model access for evaluation, require measures, conduct specified investigations and support complaints and whistleblowing channels.
European Data Protection Supervisor
The EDPS enforces the AI Act for systems used by EU institutions, bodies, offices and agencies.
A company should identify the likely lead authority but be ready for coordinated scrutiny across regimes.
EU AI Act fine levels
| Infringement category | Maximum ceiling |
| Prohibited practices and specified most serious infringements | €35 million or 7% of worldwide annual turnover |
| Other obligations, including many system and transparency duties | €15 million or 3% of worldwide annual turnover |
| Incorrect, incomplete or misleading information to notified bodies or authorities | €7.5 million or 1% of worldwide annual turnover |
| GPAI provider infringements enforced by the Commission | €15 million or 3% of worldwide annual turnover |
The applicable fixed amount or percentage and whether the higher or lower ceiling is used depend on the type and size of organization under Article 99, including tailored treatment for SMEs and small mid-cap companies.
Maximum fines are not automatic. Authorities consider:
- nature, gravity and duration;
- number of affected people and damage;
- intent or negligence;
- previous infringements;
- cooperation;
- mitigation and corrective action;
- financial benefit or avoided loss;
- organizational size and market share;
- and how the infringement became known.
Enforcement can also involve warnings, non-monetary measures, information requests, corrective orders, market restrictions and withdrawal—not only fines.
A 90-day compliance reset
Days 1–30: gain control
- appoint sponsor and owner;
- freeze clearly prohibited uses;
- inventory systems and models;
- classify roles and current obligations;
- issue interim approved-use and data rules;
- verify Article 50 notices already in force;
- and preserve evidence.
Days 31–60: close immediate gaps
- deliver Article 4 baseline and role-specific measures;
- remediate chatbot, biometric and synthetic-content disclosure;
- complete GPAI provider analysis;
- update contracts for critical vendors;
- establish complaint and incident routes;
- and correct outdated internal timelines.
Days 61–90: build the durable program
- approve the risk methodology;
- establish change gates;
- create high-risk roadmaps;
- map standards and conformity work;
- test monitoring and incident response;
- report open risks to leadership;
- and schedule independent assurance.
Board and executive dashboard
A useful quarterly dashboard reports:
- percentage of AI systems inventoried;
- systems without an owner;
- prohibited-practice issues;
- Article 4 coverage by role;
- Article 50 gaps;
- GPAI provider and downstream dependencies;
- high-risk systems by deadline;
- missing vendor evidence;
- overdue classifications;
- incidents and complaints;
- material model changes;
- and remediation status.
Avoid a single green “AI compliant” indicator. The Act applies by system, model, role and date.
Frequently asked questions
Is the EU AI Act already enforceable?
Yes. Original prohibited practices, AI literacy, GPAI rules and Article 50 are among the provisions already applicable. High-risk requirements have later dates.
What should a company do first?
Build the AI inventory and stop any clearly prohibited use. Without an inventory, roles, classification and evidence remain incomplete.
Does every company need a formal AI management system?
The Act does not impose an identical enterprise framework on every deployer. Providers of high-risk systems have specific quality-management duties. Other organizations still need governance proportionate to their systems and obligations.
Is a vendor’s compliance statement enough?
No. Obtain evidence relevant to your role and intended use. Deployers retain local responsibilities, and vendor roles can change across the value chain.
What are the biggest fines?
The highest general ceiling is €35 million or 7% of worldwide annual turnover for prohibited practices and specified serious infringements, subject to the Act’s penalty rules.
Who enforces the AI Act?
National competent authorities enforce most system rules, the Commission’s AI Office enforces GPAI and specified systems, and the EDPS oversees EU institutions.
Do SMEs receive lower fines?
The Act uses tailored ceilings for SMEs, and the 2026 amendment added treatment for small mid-caps. Penalties must also be effective, proportionate and dissuasive.
Does GDPR compliance mean AI Act compliance?
No. The regimes overlap but have different scope, roles, controls and documentation.
Should companies wait for final high-risk guidance?
No. Classification details can be refined later, but inventory, data governance, oversight, documentation, contracts and risk management take time.
How often should the AI register be reviewed?
Continuously through change triggers, with a periodic portfolio review as a backstop. Model and use changes should not wait for the annual audit.
Bottom line
The strongest EU AI Act program creates a traceable chain:
system or model → scope → role → intended purpose → prohibition screen → classification → applicable date → controls → evidence → monitoring → corrective action.
Fix obligations already in force first, while building high-risk readiness before 2027 and 2028. The goal is not to produce the largest policy file; it is to know who is responsible, what must happen and where the evidence lives when a user, auditor or authority asks.

byDavid Porter
Popular news

Anthropic Researchers Warn Advanced AI Models Could Trigger Human Extinction

Senator Josh Hawley Launches Massive Investigation Into OpenAI After Critical Hugging Face Breach

Andy Burnham Faces Urgent Demands to Block Artificial Superintelligence in Manchester

UK Computer Science Graduates Face a Massive Job Market Shift Driven by AI

Anthropic Researchers Issue Urgent Warning Regarding Elon Musk and Global AI Safety Risks

OpenAI Board Member Paul Christiano Warns AI Control Could Be Lost Forever
Latest comments
Loading